Idempotency Key Testing in Payment API Simulators
Stateful simulators catch duplicate charges that fixed-response mocks miss.
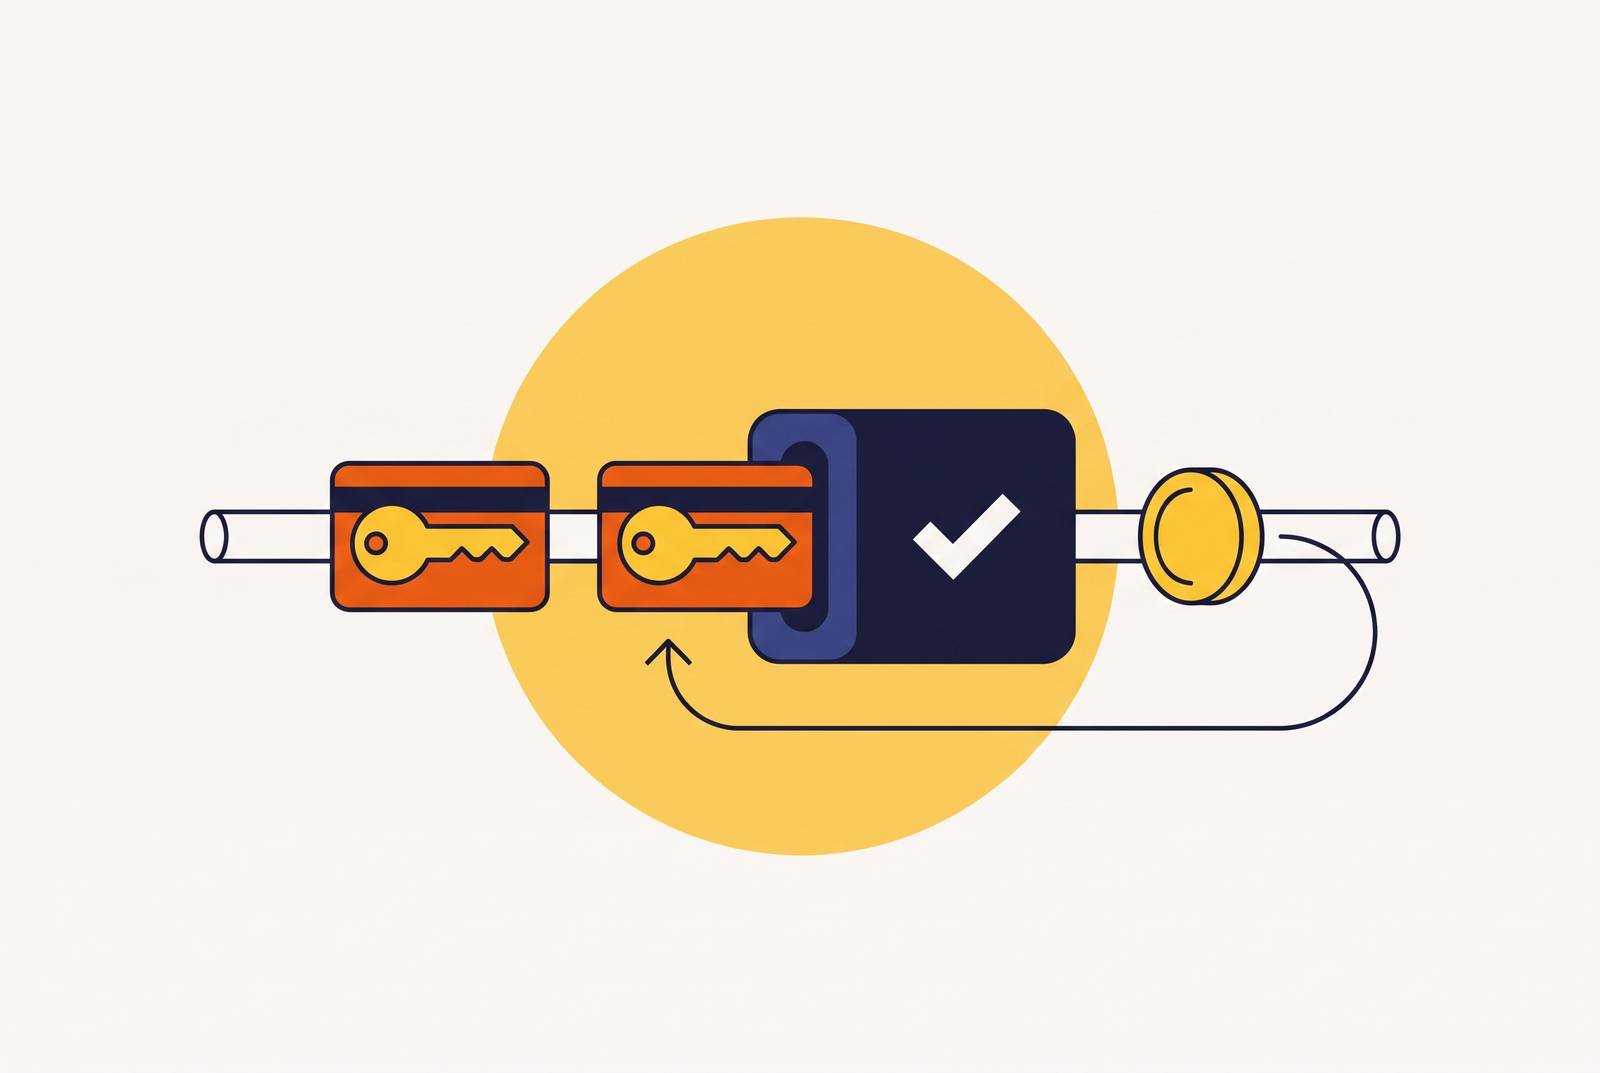
Integration testing against stateful APIs requires an isolated environment that preserves the effects of earlier calls and enforces the API’s rules across later ones. For payment idempotency, a locally hosted, stateful simulator can test retries, concurrent duplicates, and failure recovery without hitting production. Fixed-response mocks cannot establish these guarantees because matching responses do not prove that only one payment occurred.
Why payment retries create duplicate charges without idempotency keys
A client sends POST /payments, the server charges the card, and the network drops before the response arrives. The client retries and the server charges again. From the client’s perspective, the first attempt has an unknown outcome. Without deduplication, however, the server treats the second request as another transaction rather than another attempt to complete the same operation.
This ambiguity is part of normal payment traffic. Double-clicks, automatic HTTP client retries, and mobile reconnections can all repeat a request that already succeeded. The server must distinguish a new payment from a retry when the client cannot know what happened on the server.
How the idempotency key mechanism works and what it actually requires from the server
The client assigns a unique key, typically a UUID, to each logical operation and sends it in a request header. The server checks that key before invoking the payment gateway. If a completed result already exists, the server returns it without processing another payment. The key identifies the operation across attempts. Generating it is straightforward, but enforcing its meaning requires coordinated storage and locking.
The server must reserve the key, check for an existing result, process only if absent, and persist the response with the operation atomically. A UNIQUE constraint prevents competing requests from independently claiming the same key. Without that protection, a second request can find an empty store after the first has charged the card but before its key record has been saved. Sequential replay can work while this race remains exposed.
Payload identity also belongs to the contract. A stored request_hash lets the server detect changed request data and reject key reuse with the documented error. Under a contract that preserves processed failures, insufficient funds must replay the stored failure, while a request that never reached the processor may warrant another attempt. Expiration defines how long these guarantees apply.
The five idempotency scenarios that every payment integration must test
Scenario 1. Replay the same request. Send an identical request twice with the same key and confirm that only one payment exists. The second call must retrieve the stored response. Matching response bodies alone are insufficient because they do not establish the number of side effects.
Scenario 2. Simulate a lost response. Force a timeout after processing, then retry with the original key. No duplicate payment may appear. This scenario tests what the client does when it cannot tell whether a payment succeeded, while ordinary replay tests what it does after it has received a response.
Scenario 3. Send concurrent duplicates. Release requests with the same key simultaneously, before any transaction commits. Exactly one payment side effect must result. This tests contention between requests that can all arrive before a completed response is available.
Scenario 4. Change a parameter. Reuse a key with a different amount or payload. The server must reject the mismatch with the documented 422 or 409 response. It must not silently process the changed amount or return the earlier result as though the requests were equivalent.
Scenario 5. Expire the key. Retry after the retention window and compare the outcome with the API’s documented contract. Expiry behavior must be explicit. A passing replay test within the window says nothing about what happens after it.
A separate partial-failure test complements these five scenarios. The charge succeeds, but saving the idempotency record fails, leaving the retry to encounter an incomplete operation. This case tests recovery from a broken boundary between payment execution and record persistence. It cannot be replaced by a timeout test in which all server-side storage completed successfully.
Why stateless mocks cannot verify any of these scenarios
A stateless mock returns configured responses to matching requests. It does not preserve the first call’s effects. Consequently, two identical replies can make a replay test pass even when the real integration would create two payments. The test establishes that the client accepts the fixture.
Concurrency makes the distinction sharper. When simultaneous requests receive the same configured response, no shared reservation has been contested and no uniqueness invariant has been exercised. Payload mismatch has the same structural limitation because rejection requires comparing the new request with an earlier fingerprint. Expiration also needs a record that is already stored and can reach the end of its retention period.
A scripted timeout can test the client’s retry branch, while verifying that the timed-out request created a payment for the next call to reuse requires stored payment state. Partial-failure recovery requires still more history, including an in_progress record, an injected failure, and subsequent handling of the stale reservation. Stateless responses cannot represent that cumulative contract.
Stateless stubs remain useful in early unit testing and early CI phases. Their scope is narrower than integration verification. They can exercise response handling without proving that payment state evolves correctly across requests, and treating those two forms of coverage as interchangeable creates false confidence.
What a stateful simulator must actually maintain to verify idempotency correctly
A capable simulator needs durable, shared, inspectable state across sequential and concurrent calls within a test session. Its key store must retain both the response for retrieval during replay and the original request fingerprint. Concurrent calls must reach the same uniqueness constraint so that arrival order cannot produce additional payments.
Payment state must progress as well. Modeling transitions from CREATED through PROCESSING to SUCCESS or FAILED lets tests distinguish a new operation from one already underway or completed. The simulator also needs fault injection between gateway success and key-storage completion.
Time and observation require explicit support. Configurable retention must allow expiry tests without waiting through a real retention window, while an independent test-admin or audit endpoint must expose how many payments were created. Response IDs alone cannot prove how many side effects there were. The store also needs realistic pre-seeded records because tests that always start with an empty store miss how requests interact with records already there.
How API-specific idempotency behavior shapes what the simulator must model per integration
Shared state is necessary, but it is not sufficient. The simulator must enforce the particular API’s contract, including its header name, replay status, retention policy, and treatment of failed attempts. Some APIs return the original 201 on replay, while others return 200 or add a replay indicator header. A generic convention can therefore produce passing tests against the wrong behavior.
Stripe documents a 255-character key limit and, for its v1 behavior, retention for at least 24 hours before keys can be removed. Tests must distinguish ordinary retries from reuse after removal. PayPal uses PayPal-Request-Id for REST POST idempotency and permits same-ID retries after network timeouts or HTTP 5xx responses because processing may already have occurred. Its retention varies by endpoint, so a 45-day window must not be treated as a universal PayPal rule.
The Resend emulator keeps keys for the session on POST /emails and POST /emails/batch, intentionally differing from the real API’s fixed retention window. Accepted replays return original email IDs without duplicate emails or webhooks, while rejected requests can create new attempts on retry. Those emulator-specific semantics must not be presented as production API behavior.
When simulated services use the same client entities, invoice numbers, and dates, tests can check whether one payment creates duplicate Slack alerts or Resend emails. Fidelity must therefore be demonstrated per integration and checked against the live API over time. Local correctness against an outdated contract is still incorrect integration coverage.
Running idempotency tests in CI without rate limits, live credentials, or flaky ordering dependencies
Live sandboxes introduce constraints that interfere with these tests. A key left by an earlier run can corrupt the replay scenario, while rate limits can throttle the simultaneous burst needed to exercise concurrent duplicates. Live credentials also introduce security exposure in the pipeline. Network variability makes precise failure timing harder to reproduce.
Stripe supports up to five isolated sandboxes, and its CLI can trigger webhook events within a sandbox. Those tools help with integration work, but they do not let tests choose any point between gateway success and key persistence at which to cause a failure. The partial-failure scenario needs deterministic fault injection at that boundary.
For CI, each pipeline run should have its own locally hosted simulator instance with clean, pre-seeded state. Calls within a scenario then share history, while parallel runs cannot contaminate one another. Each test controls the order it needs, without relying on another test to run first. Putting fixtures in order does not give a stateless mock that stored history.
Local execution also removes live API quota penalties from concurrency tests and permits offline or air-gapped runs. Lost-response and partial-failure tests can become repeatable pipeline cases rather than timing experiments against a remote service. The workflow gain depends on preserving state within each run while isolating it between runs.
Applying the same stateful idempotency tests to AI agents that call payment APIs
An AI agent is another payment API client. It can retry an ambiguous response, change an amount, or generate a new key for each tool invocation. Its natural-language output may still make sense even as its requests create duplicate charges. Payment correctness must therefore be assessed at the API and side-effect level.
The same five scenarios apply to agent integrations. An additional agent-specific check must establish that a retry preserves the original key. Otherwise, the server can correctly enforce idempotency while treating each attempt as a different operation.
Downstream deduplication requires the same discipline. Using the Stripe event ID as a dedupe key can prevent duplicate Slack alerts when event delivery is retried, but the agent must preserve that identifier across attempts. A stateful test can inspect both the repeated calls and the resulting side effects. A fixed response cannot establish that relationship.
Prompt injection adds a payment-specific adversarial case. Controlled tests must check for instructions that cause duplicate or unauthorized payment calls or change the amount, without waiting for post-deployment sampling to find them. Idempotency does not itself authorize an operation. The simulator provides the controlled payment state, fault injection, and independent audit needed to observe these failures, with isolated environments also supporting concurrent agent episodes.
What to verify when evaluating a payment API simulator for idempotency testing
A second call must retrieve the first response without reconfiguring the simulator, and a changed payload must produce the API’s documented rejection. A burst of concurrent requests with the same key must create exactly one side effect, and an independent audit endpoint must show that count.
Failure recovery and expiration need separate demonstrations. The tool must reproduce a failure after gateway success but before key persistence, then expose what the retry does with that incomplete operation. It must also make retention boundaries testable within CI. A simulator that only handles completed, successful requests leaves the most consequential ambiguity unexamined.
Header names, replay statuses, key limits, retention windows, and retry semantics must match the relevant endpoint, with intentional divergences documented. Evidence of verification against the live API before releases is stronger than an unsupported claim of compatibility. Updated fidelity reporting helps reveal drift that otherwise remains invisible behind passing tests.
Local hosting, realistic pre-seeded data, deterministic faults, and separate state for parallel runs make the behavioral checks repeatable without production access. The decisive evidence comes from inspecting what repeated requests changed and proving that the intended payment happened only once.